A core banking system that can’t afford a minute of unplanned downtime, a security incident that has to be reported to the regulator within hours of discovery, an audit that checks whether infrastructure controls match policy on paper – banking, financial services and insurance run on IT infrastructure held to a standard most industries never face. OTS builds and manages IT infrastructure for BFSI organisations designed around that standard: continuous availability, layered security, and infrastructure built to support the compliance obligations the business already carries.
OEM Partners
Cities Delivered
Clients Served
NOC Support
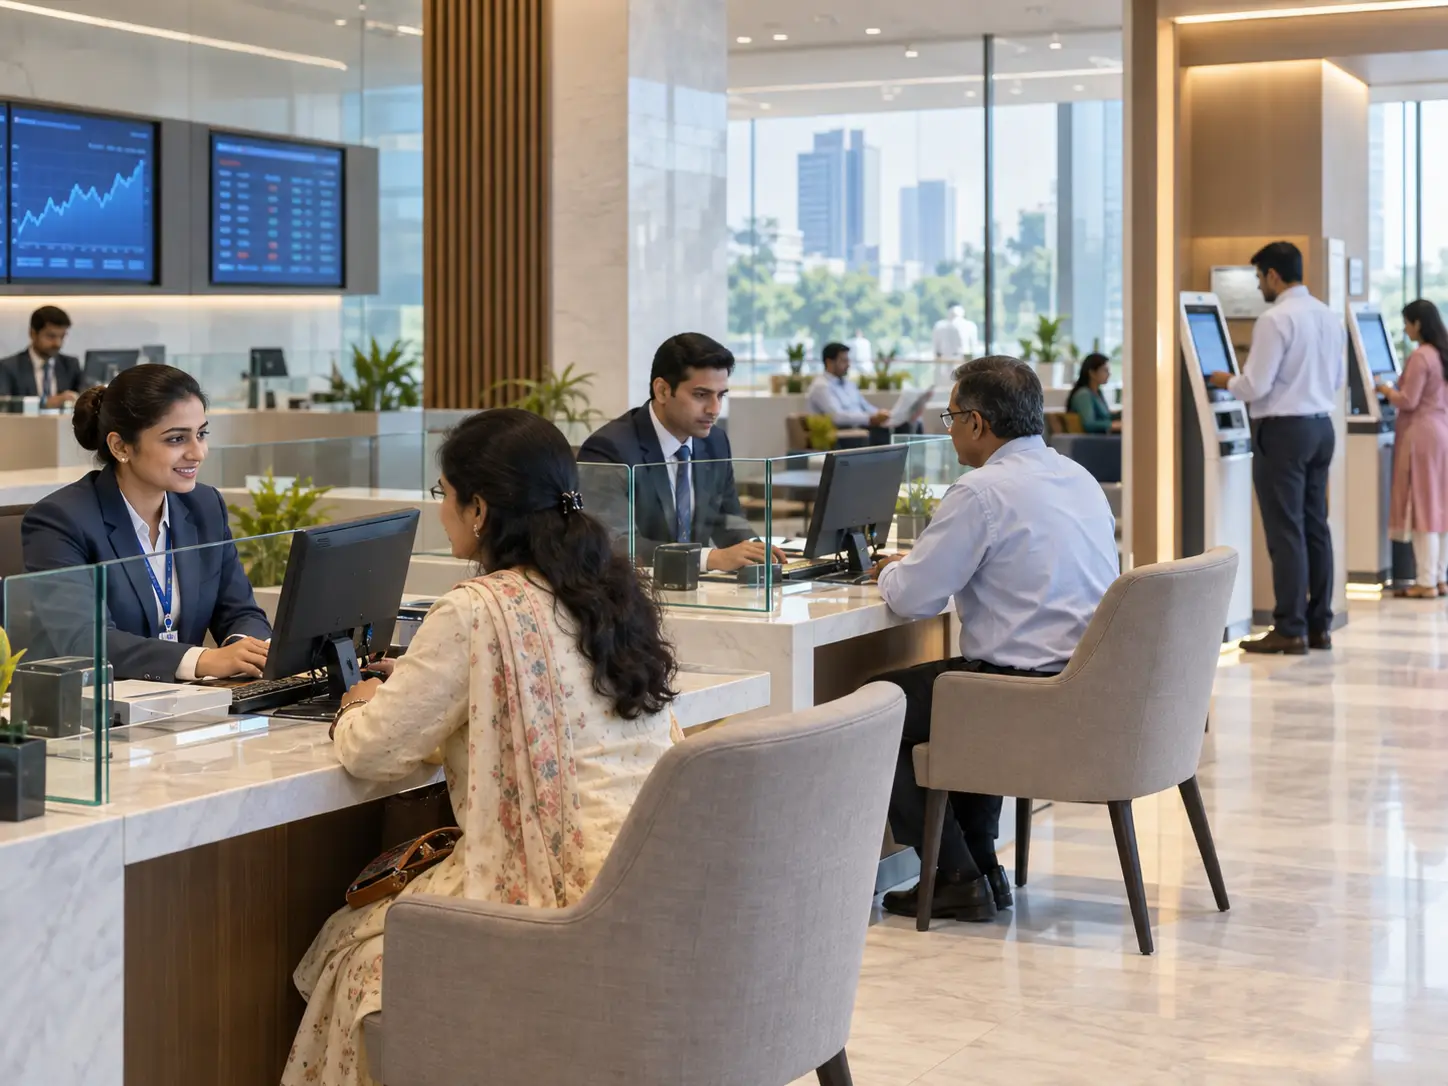
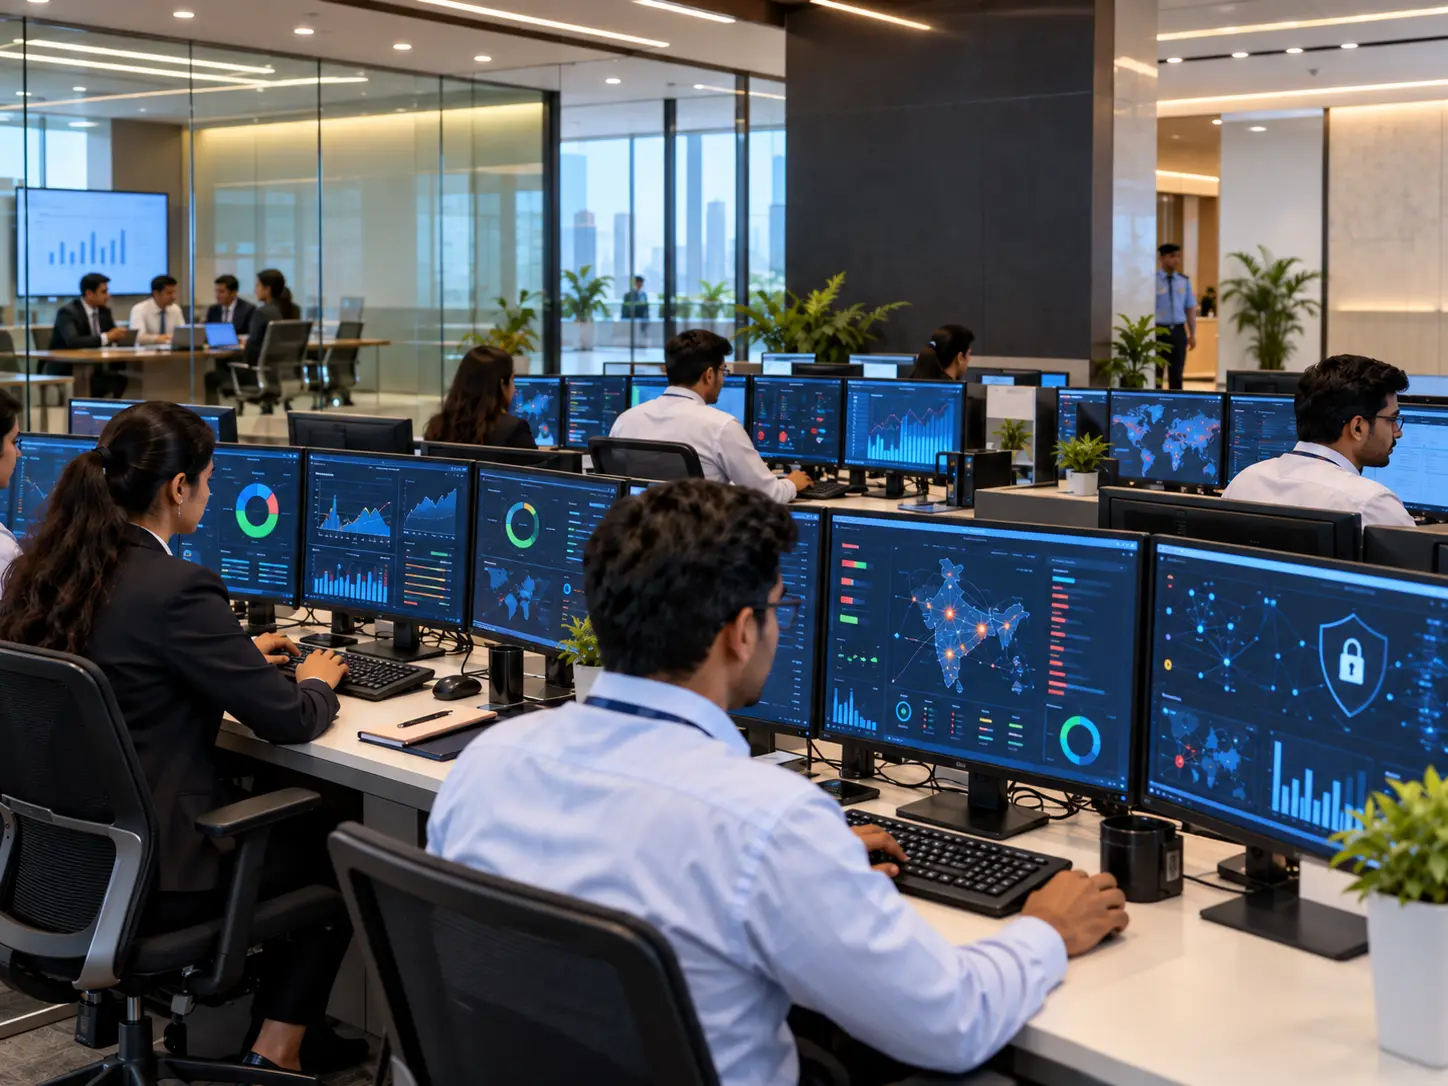
Banks, NBFCs, insurers and financial services firms operate under some of the most demanding technology mandates in Indian industry – round-the-clock monitoring expectations, security incidents that must be reported within hours rather than days, data that has to stay within defined boundaries, and infrastructure that has to hold up to VAPT and audit scrutiny on an ongoing basis, not once a year. A generic IT setup wasn’t built for that level of continuous accountability.
OTS designs, deploys and manages IT infrastructure specifically for BFSI environments – network architecture built for segmentation and resilience, data center and disaster recovery infrastructure sized for true business continuity, and monitoring built to support the always-on visibility regulators expect. It’s infrastructure engineered around what financial services actually has to prove, not just what keeps the lights on.
BFSI IT runs into a specific set of pressures that a standard commercial IT setup isn’t built to absorb:
Infrastructure expected to support round-the-clock threat detection and incident response, not business-hours coverage.
Security incidents that may need to be reported to regulators within hours of discovery, leaving no room for delayed detection.
Sensitive customer and transaction data that has to stay within defined geographic and regulatory boundaries.
Infrastructure that has to withstand regular vulnerability assessment and penetration testing, not a one-time certification.
Outages in core banking, payments or policy systems that affect customers and carry direct regulatory exposure.
Older core banking or policy administration systems that still need to run securely alongside newer platforms.
A structured six-stage process runs behind every BFSI infrastructure engagement, from a single branch upgrade to a multi-location core banking environment.
Review existing infrastructure, security posture and regulatory obligations before recommending any changes.
Understand transaction volumes, uptime requirements and the specific compliance framework the business operates under.
Design network, data center and security architecture for segmentation, resilience and auditability from the ground up.
Deploy and migrate infrastructure with minimal disruption to live financial operations and customer-facing systems.
Test infrastructure against vulnerability assessment and penetration testing standards before it goes into full production use.
Provide round-the-clock monitoring, maintenance and support, backed by 24×7 NOC coverage.
Ten capabilities addressing the infrastructure demands specific to banks, NBFCs, insurers and financial services firms.
Secure, segmented network architecture built to isolate critical systems and limit exposure across branches and data centers.
Data center infrastructure and disaster recovery built for the continuous availability core financial systems require.
Security architecture built to support ongoing vulnerability assessment, penetration testing and continuous monitoring obligations.
Infrastructure monitoring built for round-the-clock visibility, supporting the fast incident detection and response timelines BFSI operates under.
Server and storage infrastructure sized for transaction volumes, core banking workloads and regulatory data retention.
Cloud and hybrid environments architected with data localisation and segregation requirements built in from the start.
Secure, standardised devices and access management for branch, back-office and field staff.
Physical security and surveillance across branches, ATMs and data center facilities.
Backup and continuity infrastructure built to keep core systems recoverable, not just backed up on paper.
Ongoing infrastructure management across branches and data centers, under one accountable team.
Infrastructure that keeps core banking, payments and compliance systems available, secure and audit-ready – because in BFSI, a lapse is a regulatory event, not just downtime.
Infrastructure architected for the continuous uptime core financial systems and customers depend on.
Segmented, monitored infrastructure built to support ongoing testing and audit requirements.
Round-the-clock monitoring that supports fast detection and response, rather than discovering issues after the fact.
Architecture and documentation built to hold up under regulatory review, not assembled after an audit notice.
Proactive monitoring and disaster recovery infrastructure that reduce the risk of disruptive, reportable outages.
Infrastructure across branches, data centers and back-office systems managed under a single team.
Infrastructure demands differ across the sector – a cooperative bank branch and a multi-city NBFC don’t run the same environment. OTS structures BFSI infrastructure to match the organisation, not a fixed template.
matches the one-line “positioning statement, not a generic alternative” pattern used in this exact spot on every other industry page – e.g. Healthcare’s “IT infrastructure built around clinical uptime and patient data protection – not a generic commercial setup adapted after the fact.
Banks and financial services firms typically need segmented, resilient network infrastructure, data center and disaster recovery capacity, continuous security monitoring, and infrastructure built to support ongoing vulnerability testing and audit requirements.
Yes. Infrastructure can be architected with continuous monitoring and 24×7 NOC coverage built in, supporting the fast incident detection and response timelines financial services regulation expects.
Yes. Cloud and hybrid infrastructure can be designed so sensitive customer and transaction data stays within the geographic and regulatory boundaries the business is required to maintain.
Yes. Infrastructure across branches, back-office systems and data centers can be managed under one accountable team, rather than fragmented, branch-by-branch vendor relationships.
Infrastructure is architected and documented to support ongoing VAPT cycles, so testing validates a system built for scrutiny rather than one assembled ahead of an audit.
Yes. Disaster recovery infrastructure is built to keep core financial systems recoverable within the continuity requirements the business and its regulator expect.
From network and data center to cybersecurity, disaster recovery and 24×7 monitoring, talk to OTS about IT infrastructure built for the availability and security standards BFSI is held to.
Services
Solutions
Industries